Introduction. I've never used Windows. I decided to start my acquaintance with Windows XP and its default applications. I was interested in Internet Explorer, and it will be discussed further.
Why do I need a start if I have Internet Explorer? ;)
Part 1. Old vulnerability
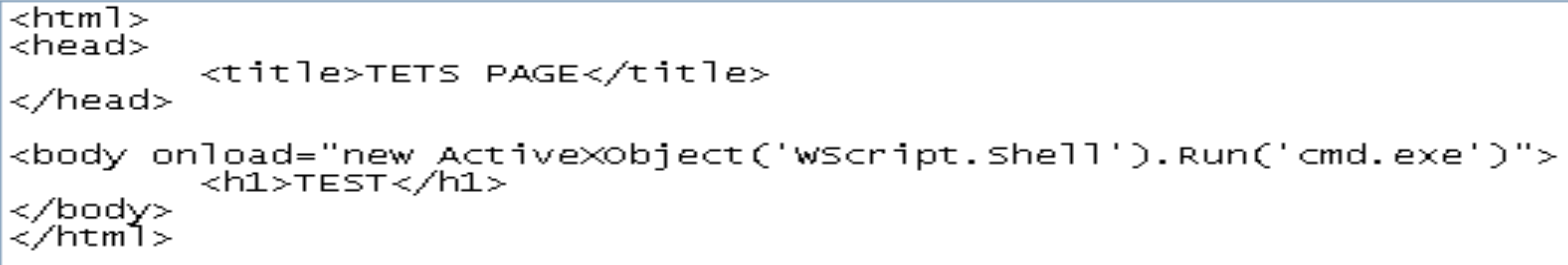
I'm not used to using file managers. Out of habit, I wrote the path to the folder I wanted to view in IE using file protocol. And then I suspected something strange ;)
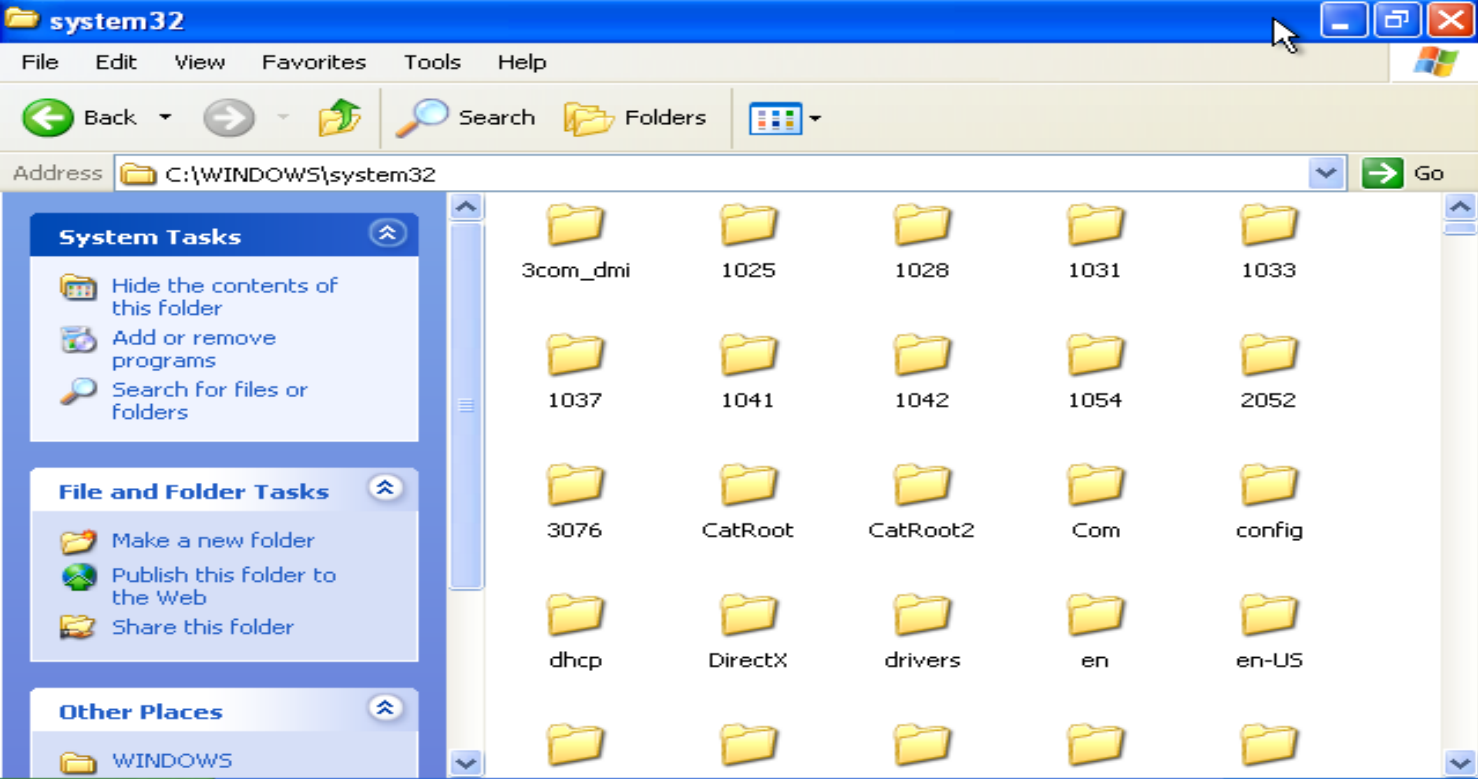
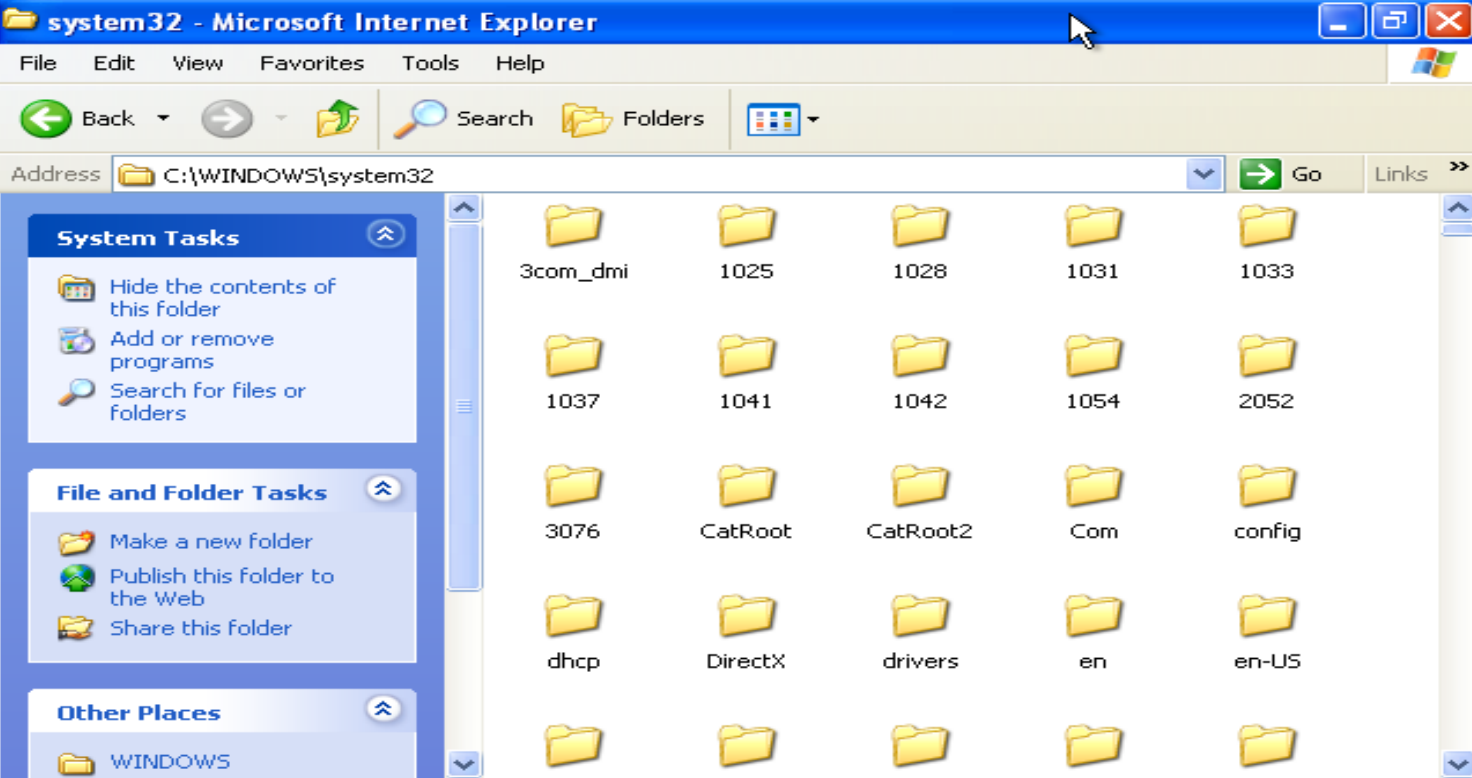
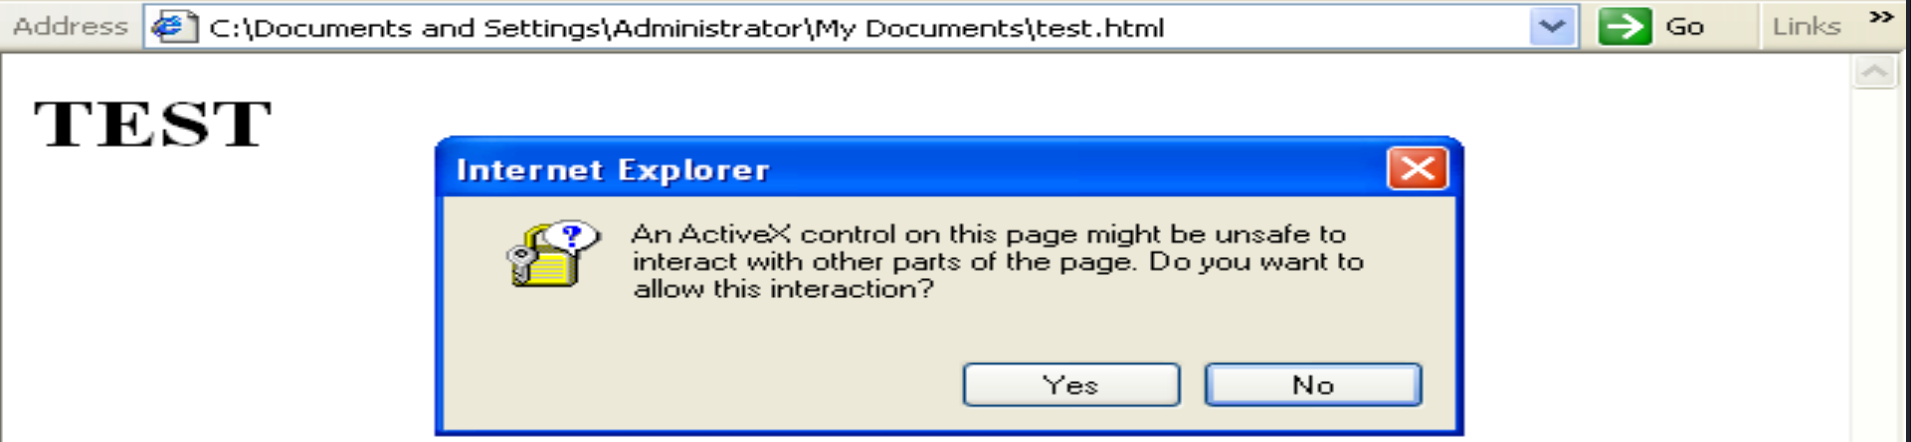
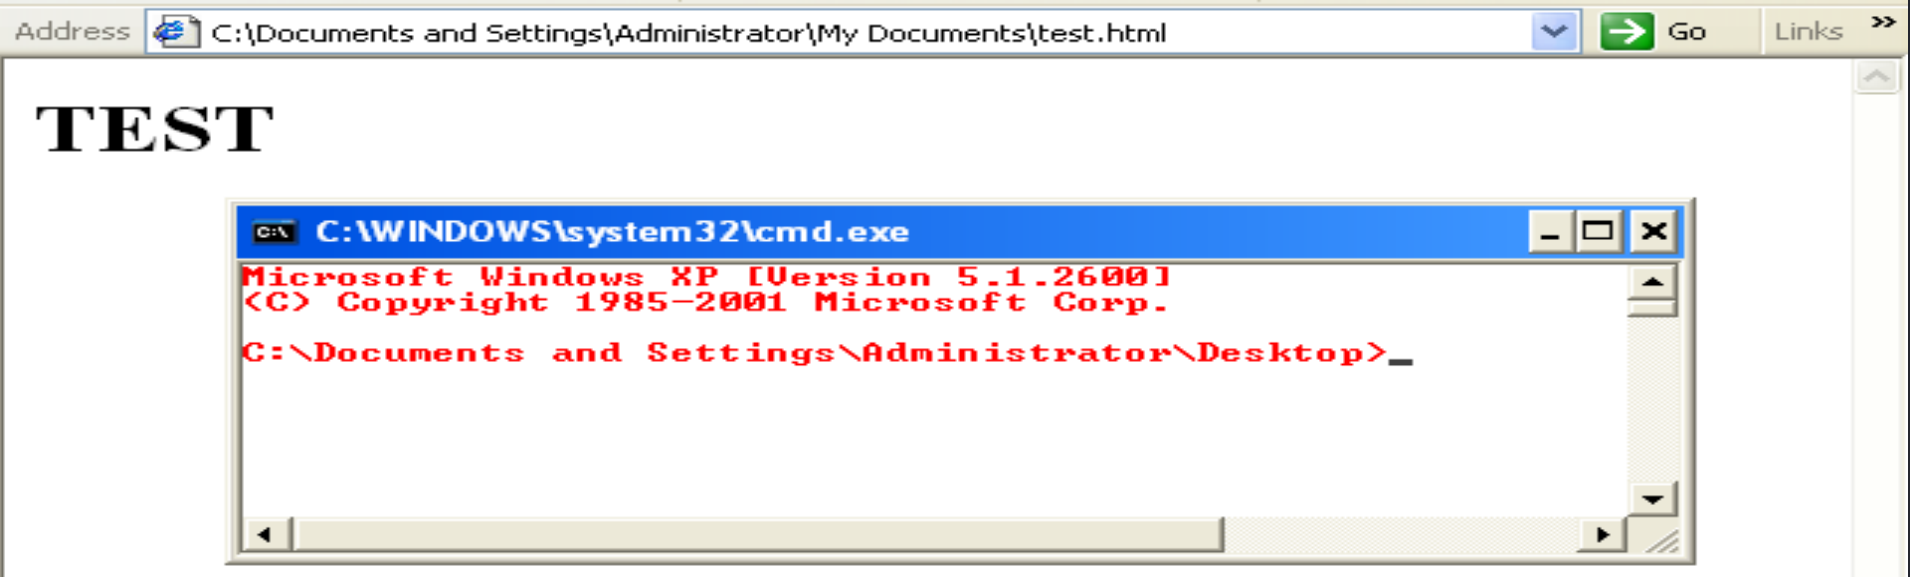
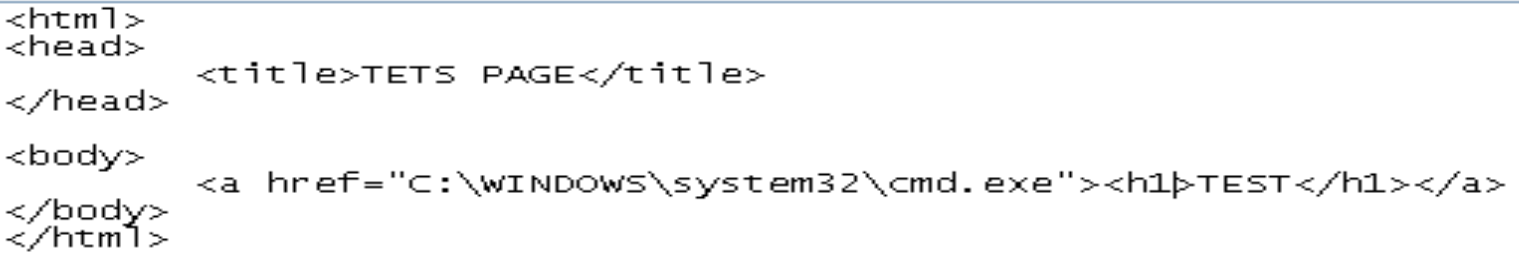
I decided to run a couple of tests to observe the behavior:
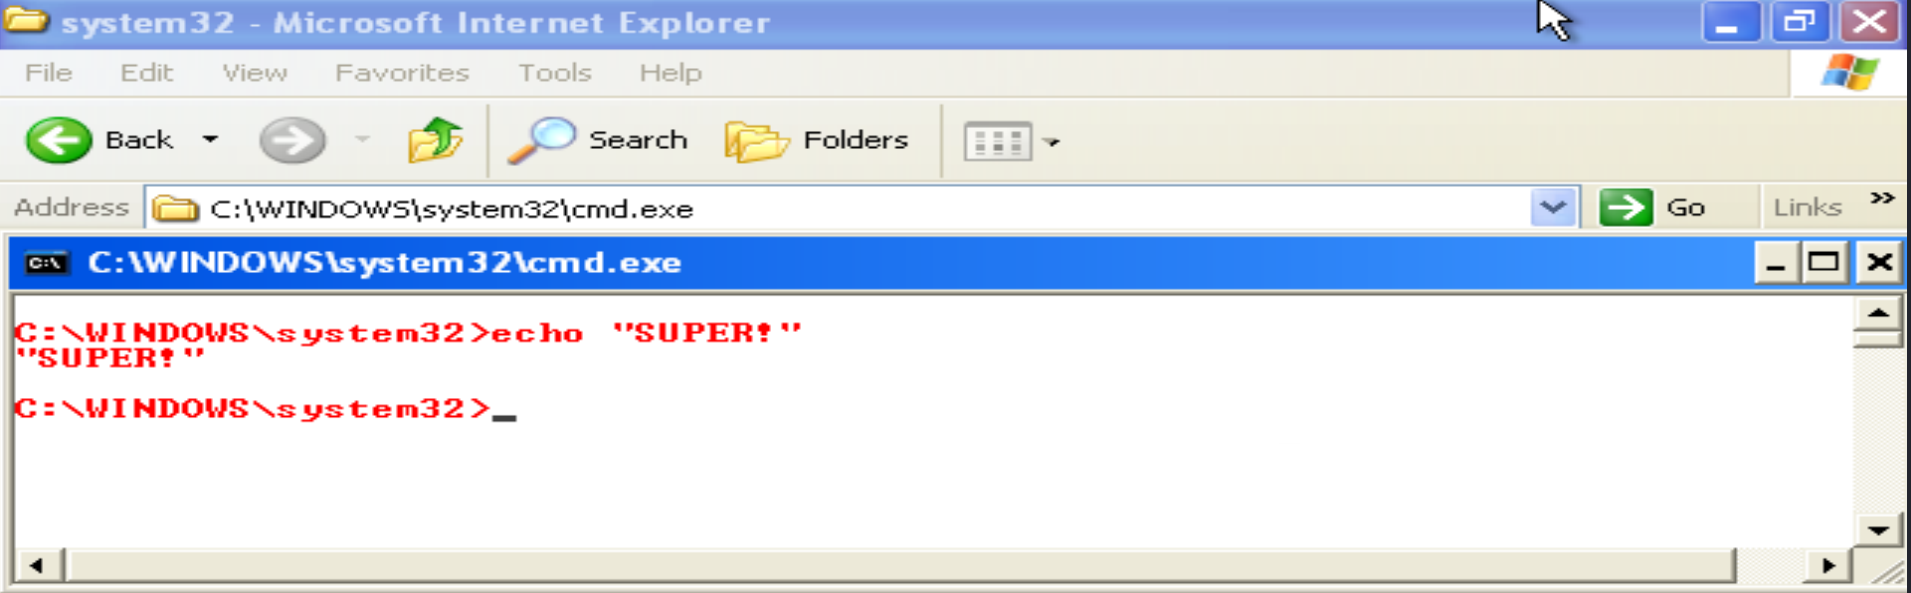
- URL:
C:\WINDOWS\system32\cmd.exe- Run cmd.
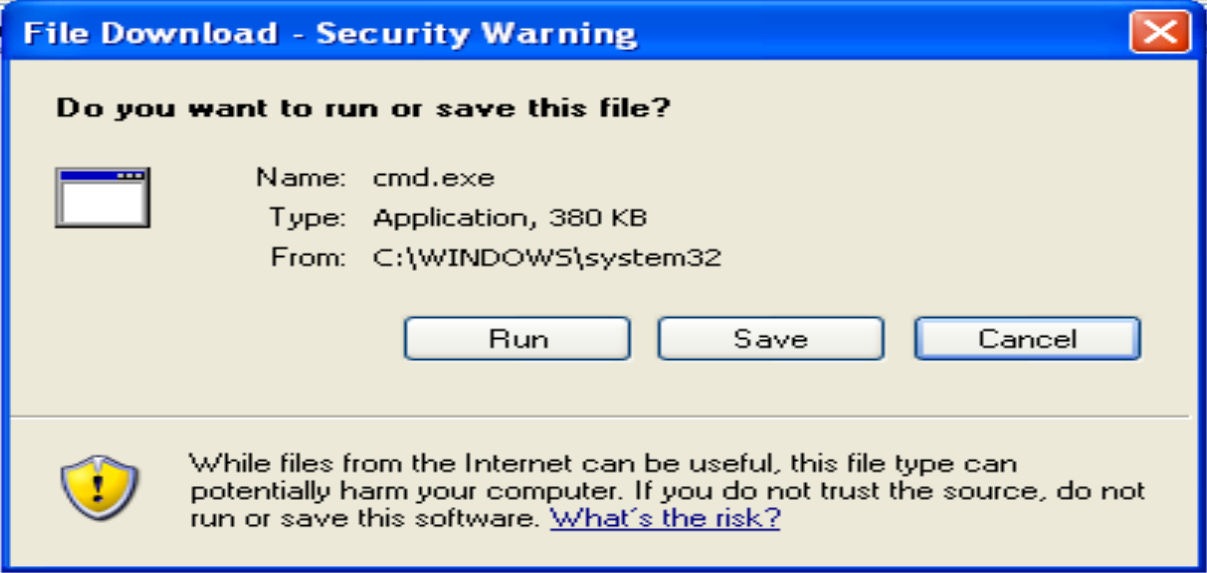
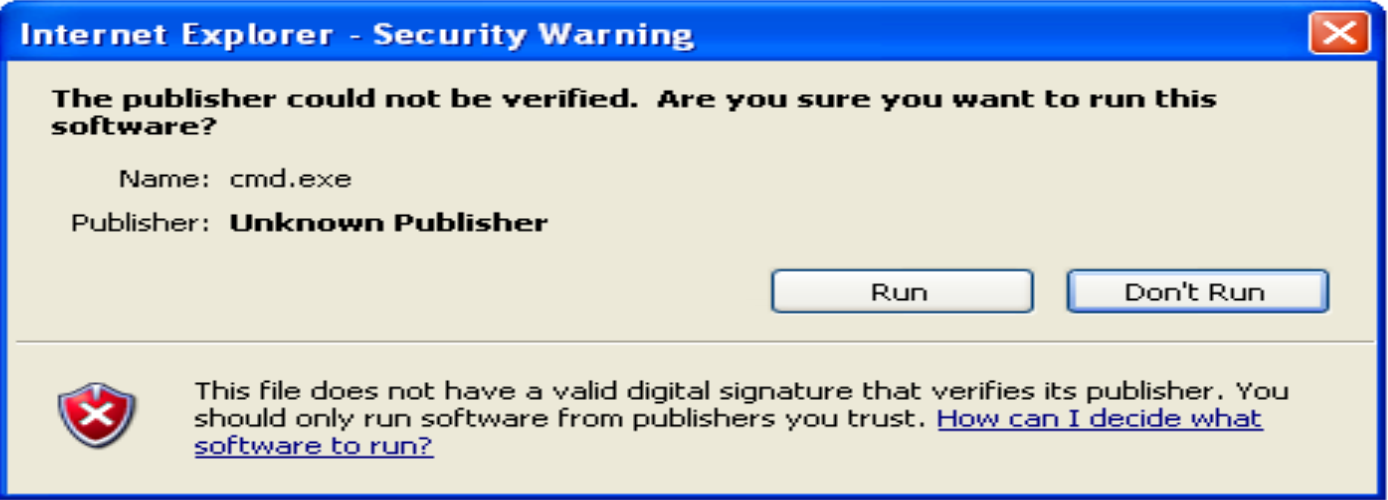
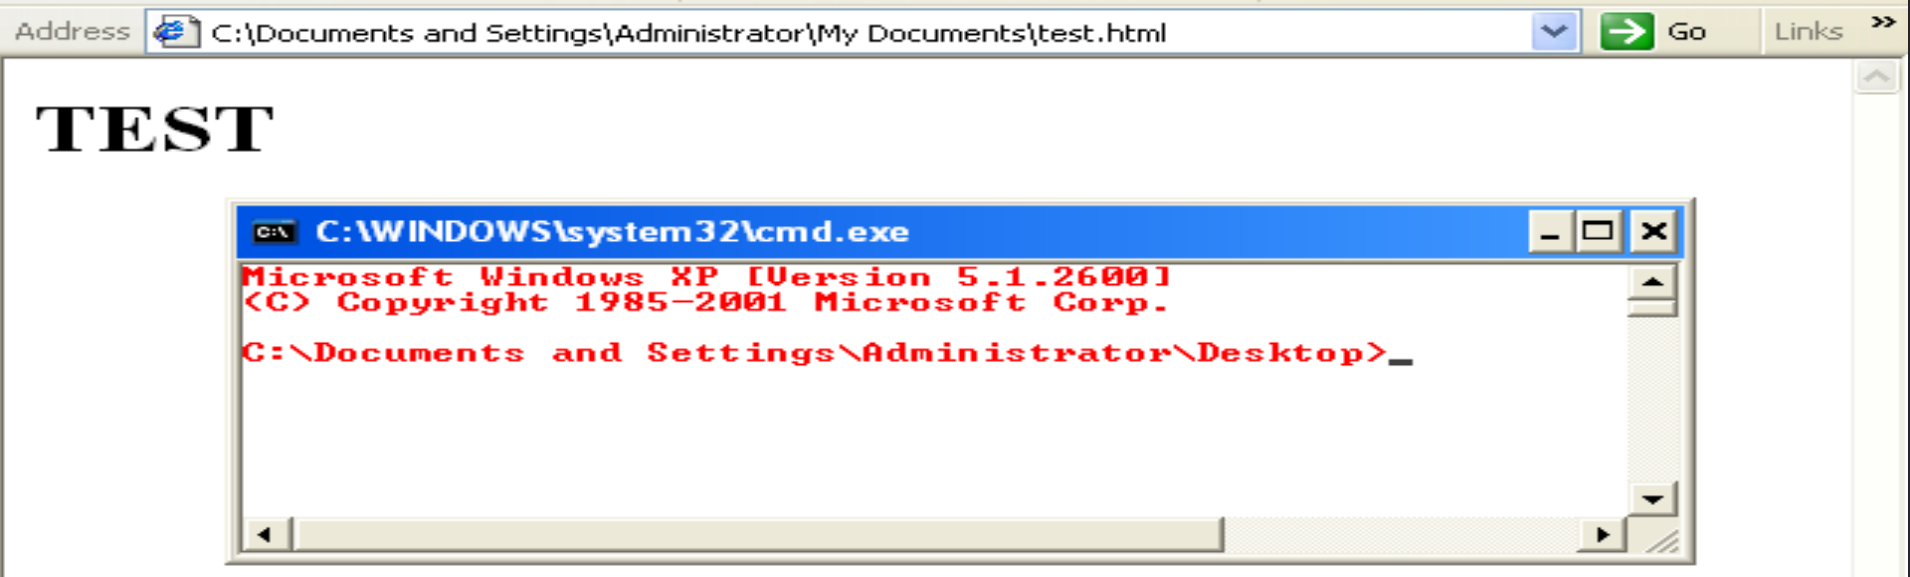
Part 2. Slightly reverse (Let's figure out why you can run applications from the browser)
- We launch ie and look at the running processes.
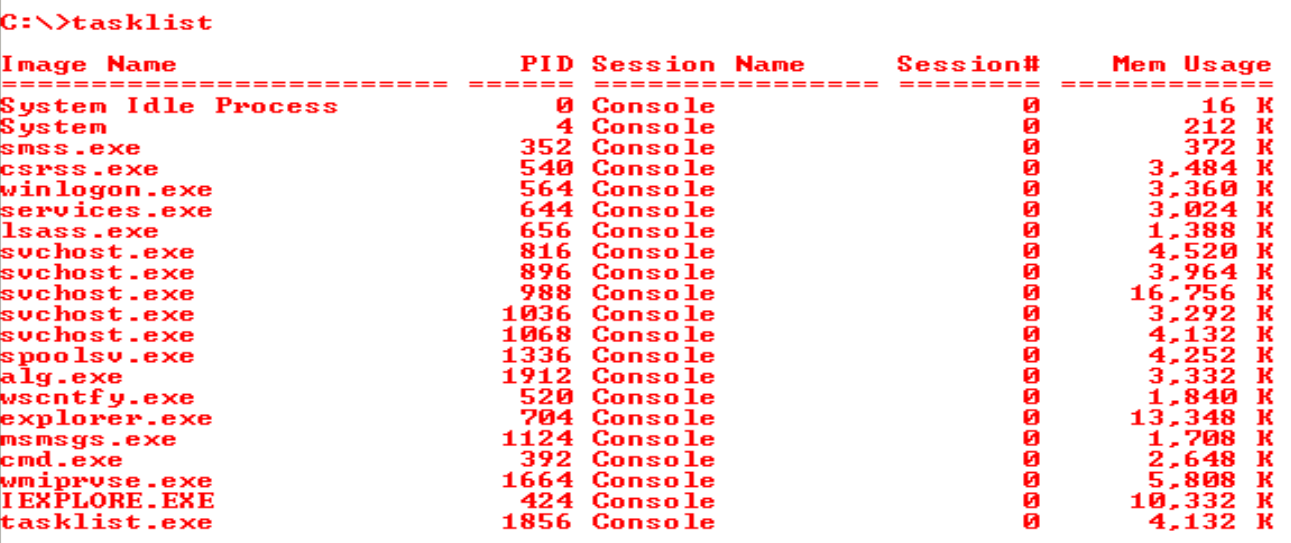 2. By its PID, we find the location before it.
 3. I pulled it out
iexplore.exe - there is no logic for processing the url string, it works as a loader.
-
I went to reverse
shdocvw.dll(since it's an engine for ie). -
sym.SHDOCVW.dll_HlinkFrameNavigateNHLis a function that breaks it down into different protocols. Defines the protocol type viafcn.7e2b1da0
0x7e302c71 call fcn.7e2b1da0
0x7e302c76 cmp eax, 9
0x7e302c79 jne 0x7e302cc9
We determine the similarity with URL_SCHEME.
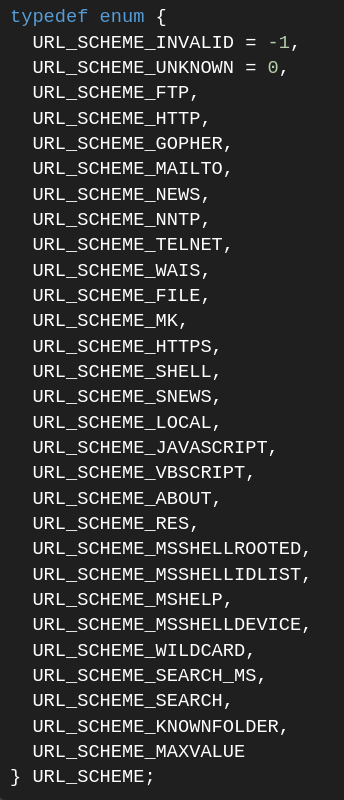
That is, if eax != 9, then jump to 0x7e302cc9.
sym.SHDOCVW.dll_HlinkFrameNavigateNHL (ShellExecuteA) - launching applications:
- We get the source string, string length:
0x7e302c4b push dword [lpString]
0x7e302c51 call dword [sym.imp.KERNEL32.dll_lstrlenW]- Copy the string to the buffer:
0x7e302cd4 push esi
0x7e302cd5 push dword [lpString]
0x7e302cdb lea eax, [var_1254h]
0x7e302ce1 push eax
0x7e302ce2 call edi- From Unicode to ANSI
0x7e302d15 push esi
0x7e302d16 lea eax, [lpFile]
0x7e302d1c push eax
0x7e302d1d lea eax, [var_1254h]
0x7e302d23 push eax
0x7e302d24 push dword [var_1ad4h]
0x7e302d2a call dword [sym.imp.SHLWAPI.dll_SHUnicodeToAnsiCP]- Transfer to ShellExecuteA
0x7e302d34 lea eax, [lpFile]
0x7e302d3a push eax
0x7e302d3b push ebx
0x7e302d3c push ebx
0x7e302d3d call dword [sym.imp.SHELL32.dll_ShellExecuteA]
P.S. ShellExecute is a function in the Windows API.
Conclusion: This is obtained by RCE which is achieved by XSS. That is why ActiveX was later killed in browsers.